Small and mid-sized enterprises (SMEs) face almost the same regulatory scrutiny as listed corporations, yet they rarely have the headcount or the budget of a Fortune 500 compliance department. As a result, well-intentioned teams often focus on checking the regulatory box and develop some standard policies instead of building processes that genuinely reduce risk. The consequences can be serious: criminal penalties, financial sanctions, lost contracts, disrupted projects, civil claims, reputational damage.
Below are the eight most common mistakes we observe when managing compliance in SMEs—and practical steps to avoid them.
1 Treating compliance as a one-off Project
Many SMEs assemble a task force for a looming audit, tick off requirements, celebrate and then disband the team until the next regulator letter arrives. Compliance, however, is a living discipline that evolves with every legal update and strategic pivot.
Action point:
- Establish an always-on compliance calendar that maps recurring obligations (e.g. audit of accounting controls, GDPR data-mapping reviews).
- Use workflow automation tools, such as Naltilia’s compliance orchestration, to assign owners and set automated reminders.
2 Relying on siloed spreadsheets
Spreadsheets multiply because they are easy to start; they become risky because they are hard to maintain. Version-conflict, hidden formula errors and limited audit trails frequently undermine regulatory evidence.
Action point:
- Consolidate control matrices, risk registers and evidence logs into a single platform with granular permissions.
- If you must export to Excel for management reporting, lock the master source in a system of record and automate the data pull.
3 Copy-pasting generic policies
Search-and-replace isn’t a policy-development methodology. A “borrowed” anti-bribery policy can ignore industry-specific red flags or national whistle-blower statutes, exposing the company during investigations.
Action point:
- Conduct a formal regulatory risk assessment (Naltilia’s module can accelerate this) to identify jurisdiction-specific requirements.
- Draft policies that map directly to those risks and update them annually—or sooner if laws change.
4 Underestimating third-party risks
A number of compliance breaches originate in the supply chain. SMEs often lack the leverage to impose detailed vendor questionnaires, but failing to ask is no longer acceptable.
Action point:
- Categorize vendors by criticality and risk profile.
- Automate data collection for due-diligence documents (ISO certifications, AML checks) and trigger remediation workflows for missing items.
5 Overlooking Culture and Training
Regulators increasingly scrutinize “tone from the top.” A perfectly written Code of Conduct carries little weight if the sales team has never read it. Yet SMEs often deliver one bulk training session during onboarding and call it a day.
Action point:
- Roll out micro-learning modules (5-10 minutes each) at regular intervals.
- Include top management in trainings to reinforce accountability.
6 Failing to document remediation efforts
Discovering a gap is only half the job; the audit trail of how it was closed is what counts. Busy teams patch the issue but forget to log evidence, leading to awkward explanations during inspections.
Action point:
- Link each remediation action to the originating risk in your compliance platform.
- Attach items (meeting minutes, updated procedures, screenshots) so that the history remains transparent.
7 Not monitoring regulatory change proactively
A new rule rarely announces itself politely in your inbox. Depending on informal newsletters or LinkedIn posts means you are always reacting late.
Action point:
- Subscribe to authoritative feeds (E.U. Official Journal, U.S. Federal Register) and set up an internal horizon-scanning process.
- Use AI-based regulatory monitoring to highlight only what is relevant to your sector and geography.
8 Equating compliance spend with value
Cutting costs by postponing control upgrades can seem rational—until a single penalty wipes out multi-year savings. Conversely, buying expensive “enterprise” solutions that require a dedicated administrator may drain resources without improving risk posture.
Action point:
- Build a cost-of-non-compliance model that factors fines, legal fees, business interruption and reputational impact.
- Opt for scalable platforms (like Naltilia) that align subscription tiers with headcount and regulatory complexity.
Getting Ahead of the Curve
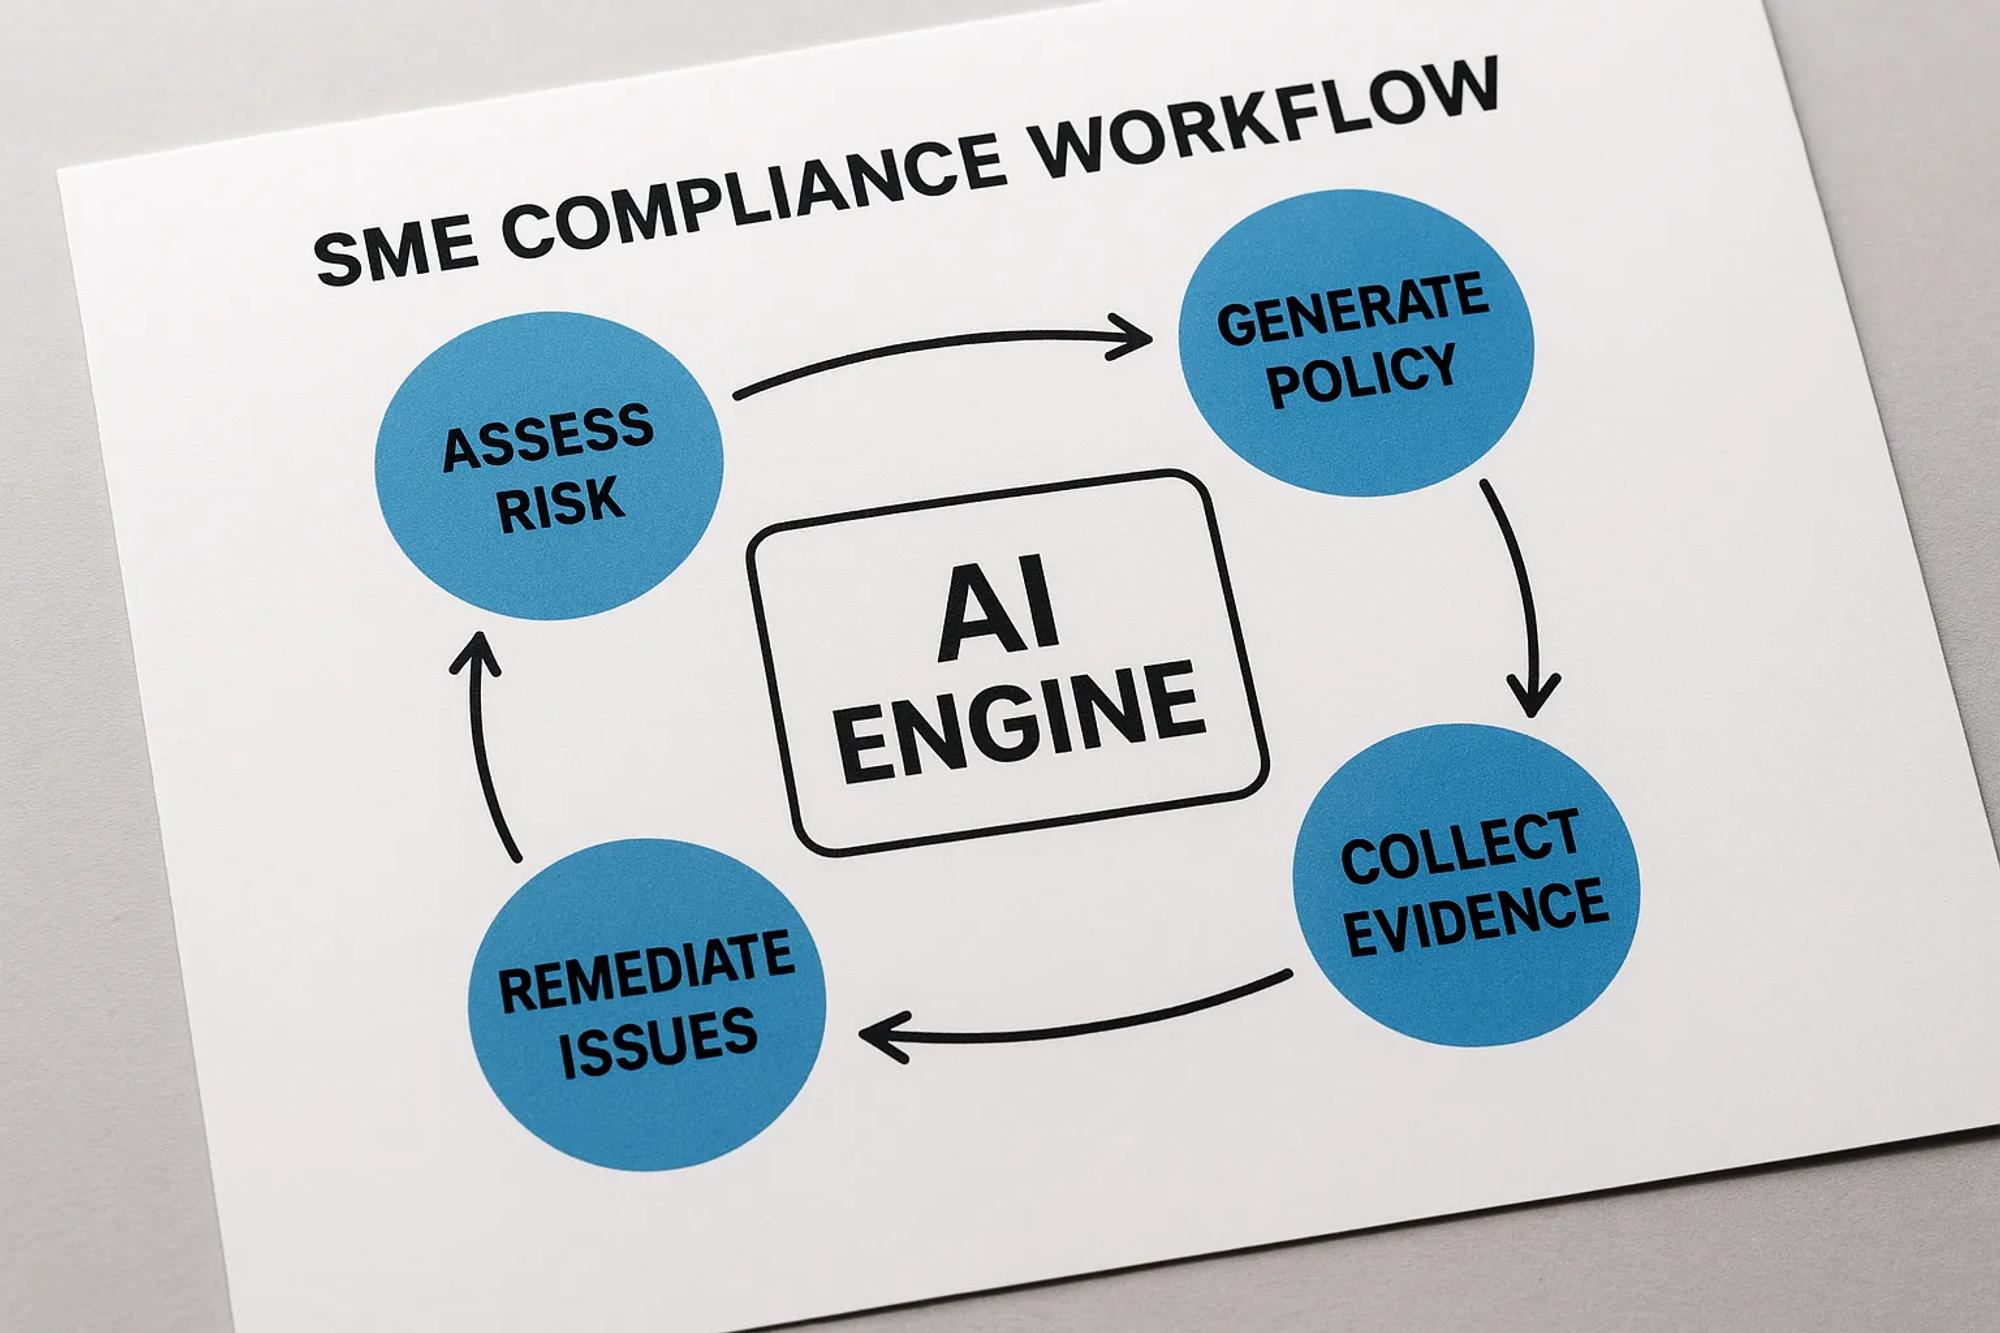
Mistake-proofing compliance is not about adding bureaucracy; it is about embedding a risk-aware mindset into everyday operations. Modern compliance teams at SMEs achieve this by combining three levers:
- Centralized data and evidence management.
- Automated workflows that scale without extra headcount.
- Continuous regulatory intelligence tailored to the company’s footprint.
Naltilia’s AI-powered platform was designed with these imperatives in mind. From automated data collection to tailor-made policy generation, the tools help compliance officers focus on strategic oversight instead of manual drudgery. Explore how the Regulatory Risk Assessment module or the Policy Builder can fit into your roadmap by asking for a demo
Avoiding the eight pitfalls above will not only keep regulators satisfied; it will free up your team to become a proactive partner in corporate strategy—demonstrating that smart, tech-enabled compliance is a competitive advantage, not an overhead.
Frequently Asked Questions
Do SMEs have to comply with the same regulations as large companies?
Largely yes. Anti-corruption, competition, AML, GDPR and criminal liability rules apply regardless of size, with certain obligations applying to certain types companies in some jurisdictions (for example, Sapin II's Article 17 establishes the obligation to build an anticorruption compliance system for companies with more than 500 employees and 100 million euros in turnover). Smaller companies are also evaluated as third parties by their larger clients, who increasingly demand evidence of a working compliance programme before signing.
What is the most common compliance mistake in SMEs?
Treating compliance as a one-off project. A task force prepares for an audit, ticks the boxes, and disbands until the next regulator letter. Compliance obligations recur: accounting control reviews, GDPR data mapping, third-party re-evaluations, training refreshers. Without an always-on calendar with named owners and reminders, evidence gaps reappear within months.
Can an SME run compliance on spreadsheets?
It can start that way, but spreadsheets become a liability quickly: version conflicts, hidden formula errors, no audit trail, no permissions. Regulators and auditors ask who changed what and when. A single system of record for the risk register, control matrix and evidence log, with Excel used only for exports, is the practical minimum for a defensible programme.
How should an SME manage third-party compliance risk?
Categorise vendors, distributors and agents by criticality and risk profile, then scale due diligence accordingly: light checks for low-risk suppliers, documented integrity checks and contractual clauses for high-risk intermediaries. Automate the collection of due diligence documents (certifications, AML checks, ownership information) and trigger a remediation workflow when items are missing or expired.
How much compliance training does an SME need?
More than one onboarding session. Regulators look at whether exposed populations are identified, trained and refreshed, and whether management takes part. Short micro-learning modules of five to ten minutes at regular intervals, targeted by role and risk exposure, work better for small teams than an annual bulk session, and produce completion evidence that is easy to retain.
How do you calculate the cost of non-compliance?
Add up the direct and indirect costs of a realistic incident: fines and penalties, legal and forensic fees, business interruption, lost contracts or exclusion from tenders, and reputational impact on clients and financing partners. Compare that figure with the cost of the controls that would have prevented it. In most SMEs, one incident exceeds several years of prevention spend.